Every new vulnerability, matched to your software and sent to the team that owns it.
Secrook checks the public vulnerability sources every hour, finds the ones that affect the products you run, and sends the owning team what to fix and by when. Hosted by us, or on your own server with the Max plan.
Every hour
Public vulnerability sources and vendor advisories are checked around the clock.
Matched by version
A finding is raised only when your installed version is affected.
One email per team
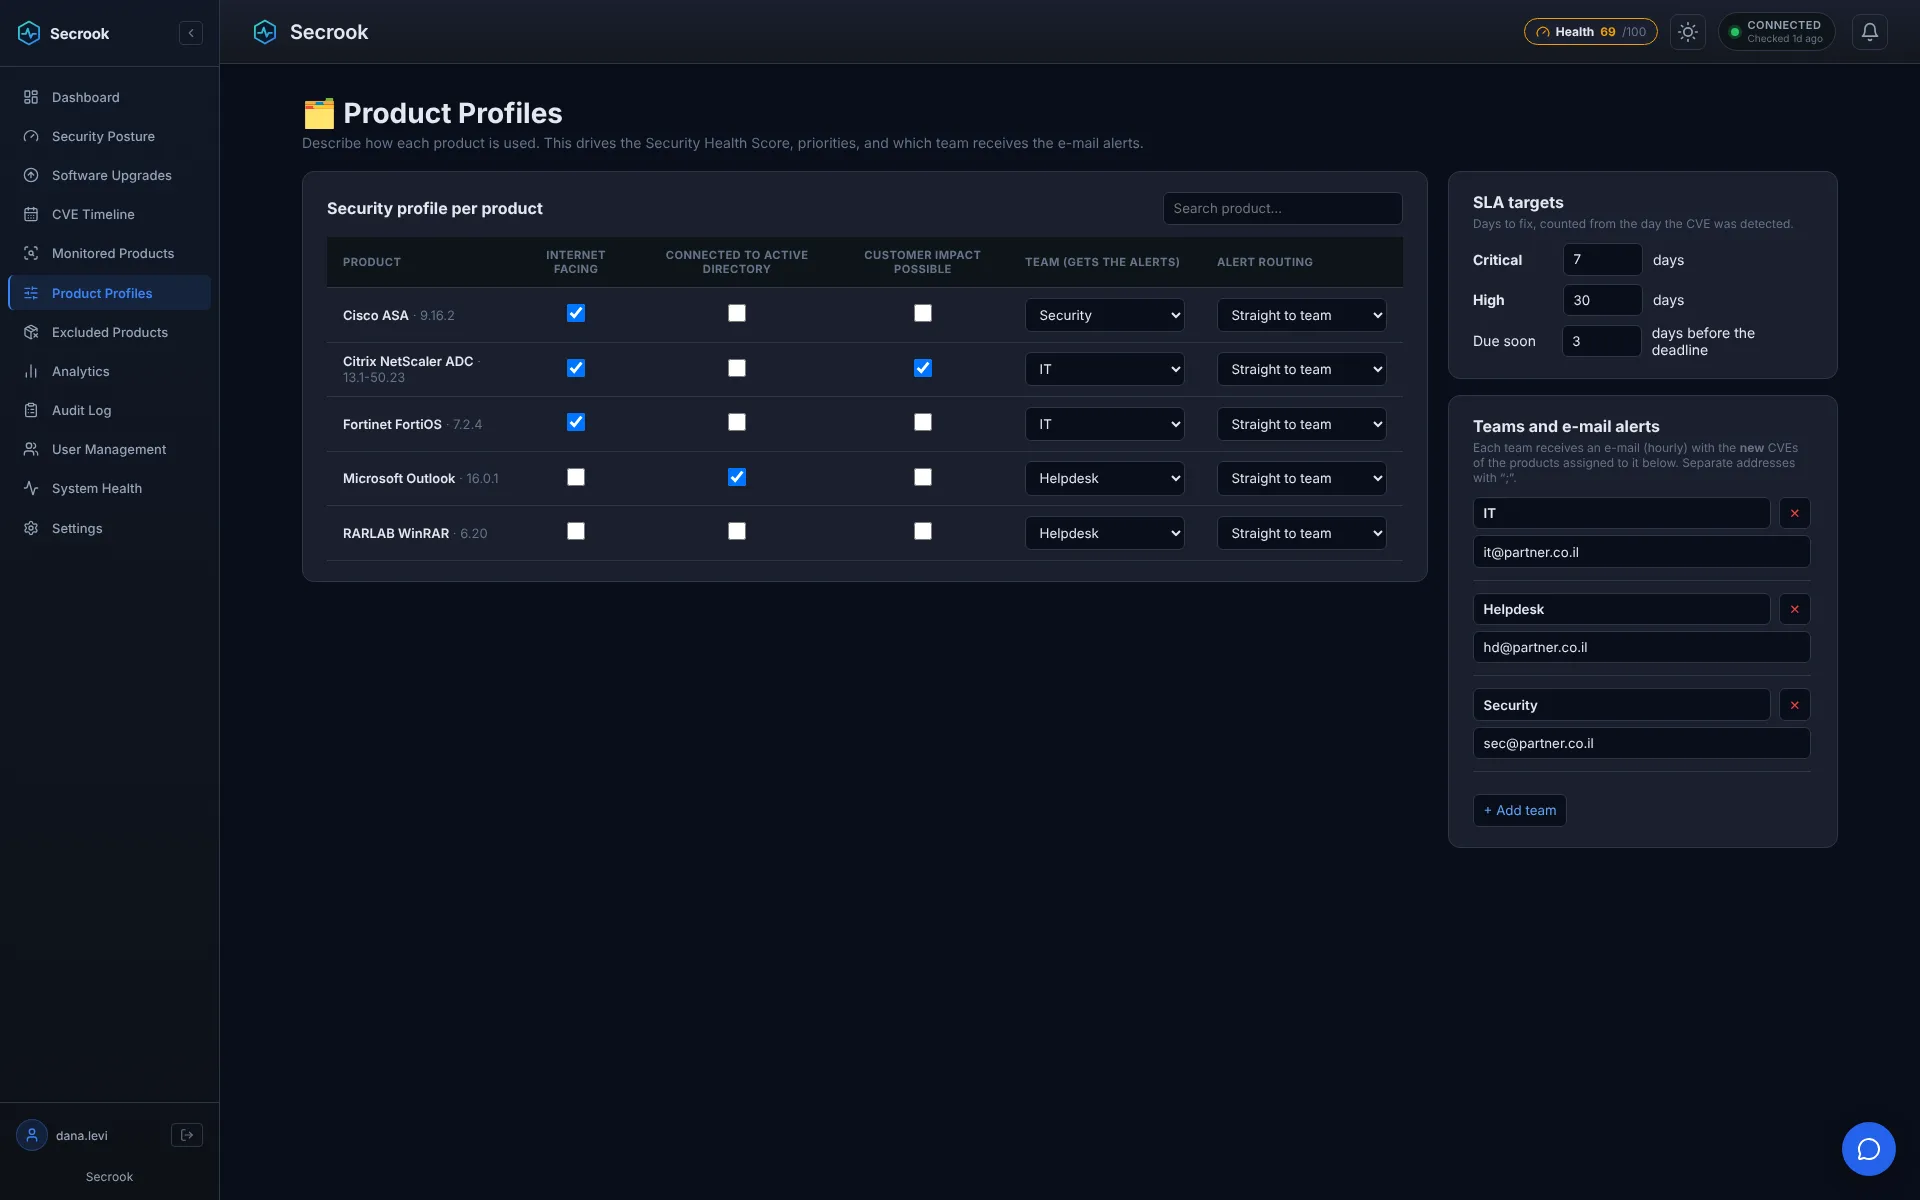
Each team receives only the findings for the products it owns.
7-day trial
Try it on your own product list before you decide on a plan.
Advisories read straight from the vendor
These vendors have a dedicated advisory feed. Every other vendor and product is found through the public vulnerability database.
Vendor and product names are trademarks of their owners. Their use here does not imply endorsement.
What your team receives
One e-mail per team, sent as soon as new findings appear for the products it owns. Nobody else is disturbed.
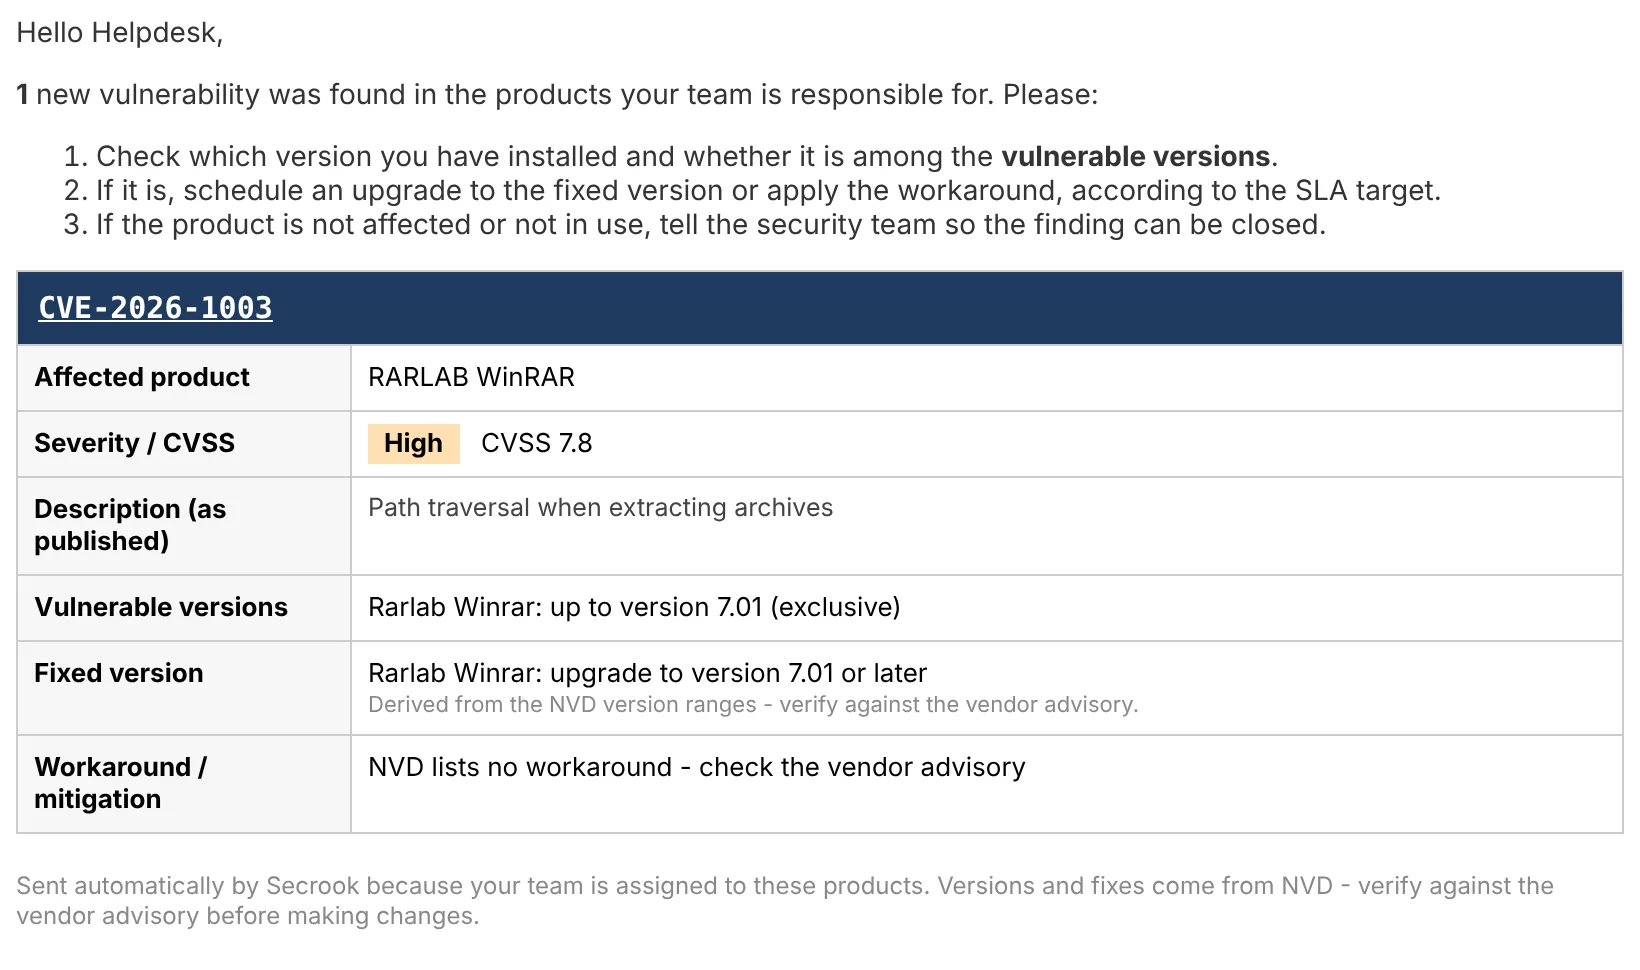
Written for the person who has to act
- Which product, which version, and why it matters to you.
- The version that fixes it, taken from the Software Upgrades.
- A CSV attached with the due date for each finding.
How it works
Four steps, every hour, without anyone opening a spreadsheet.
1. Collect
Public feeds and vendor advisories
2. Match
Your products and versions
3. Assign
The owning team, with a due date
4. Track
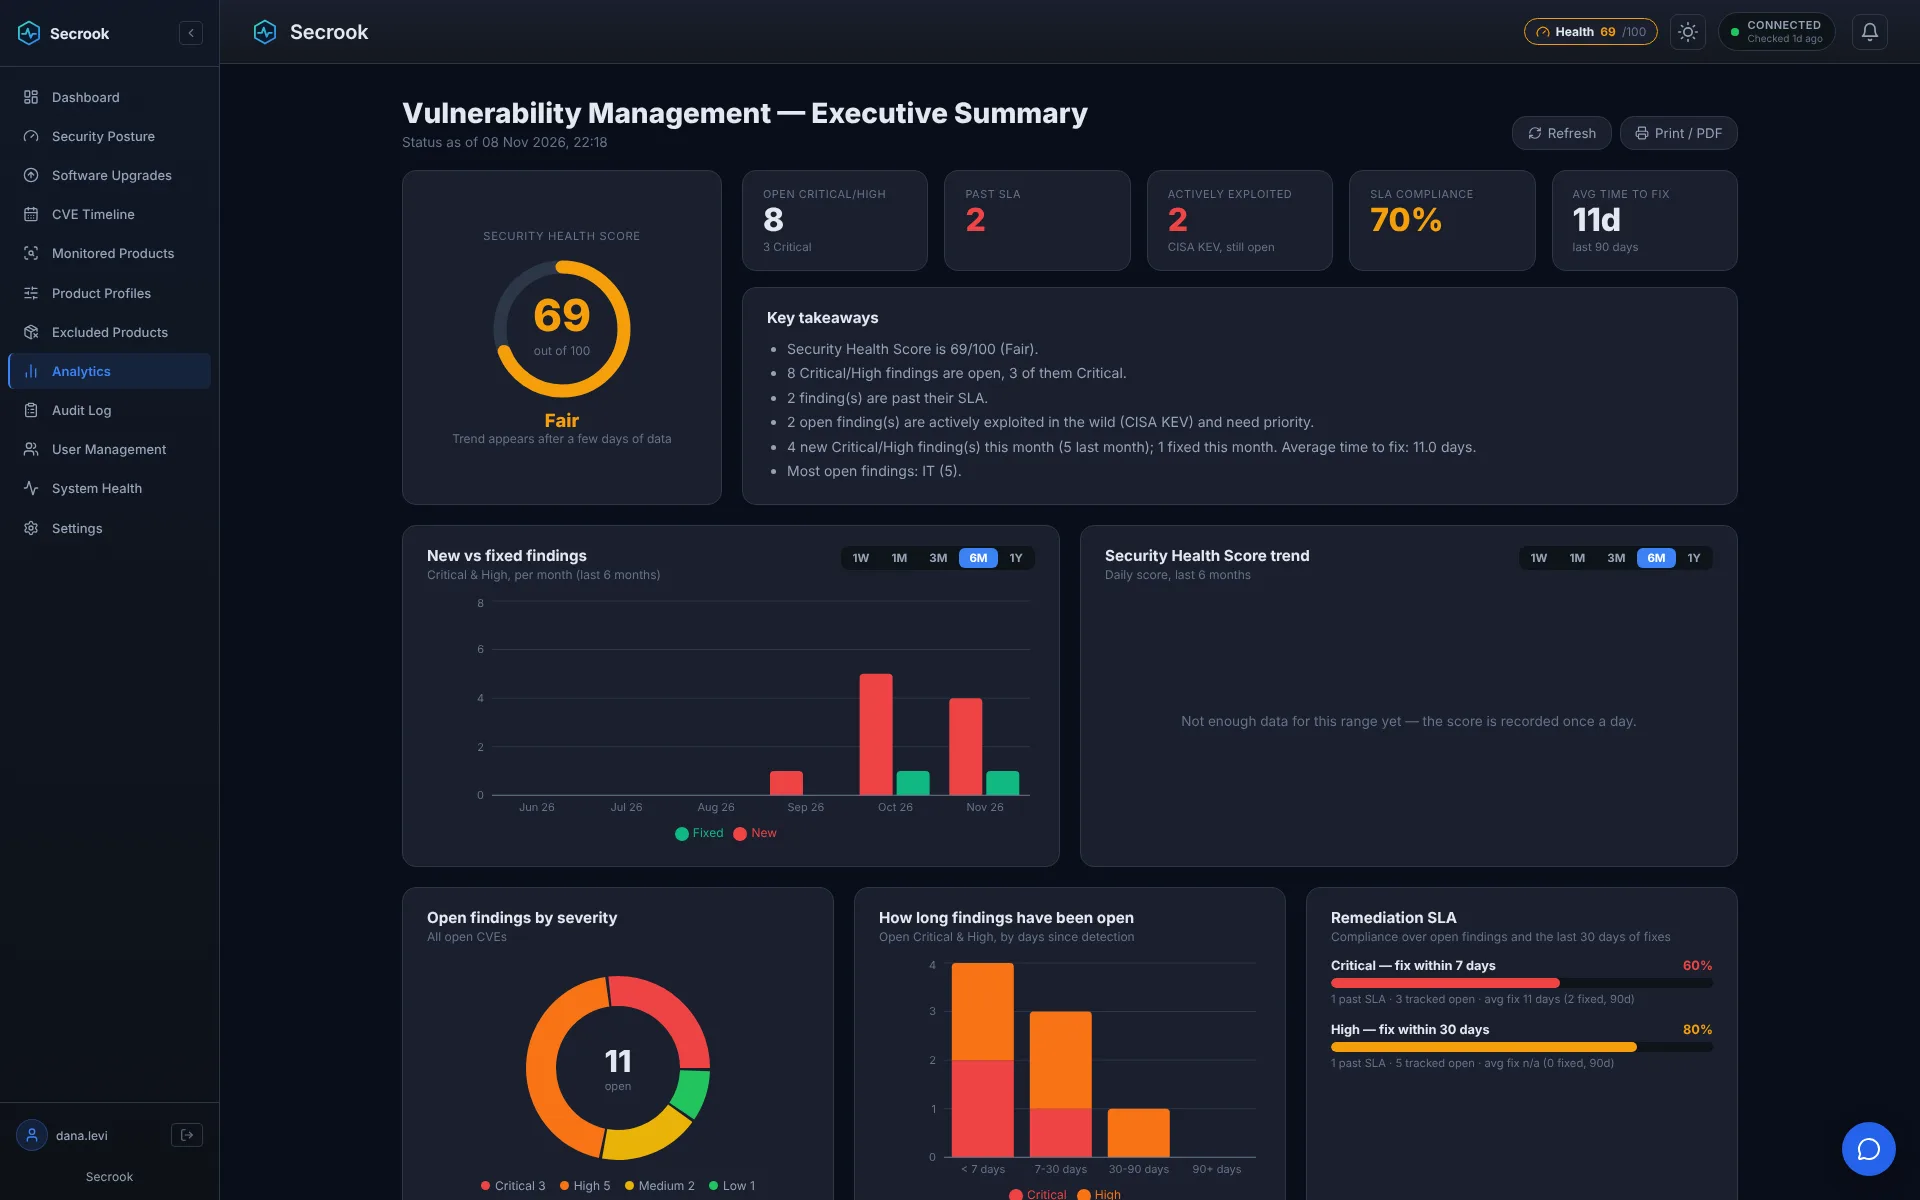
Open, overdue and fixed
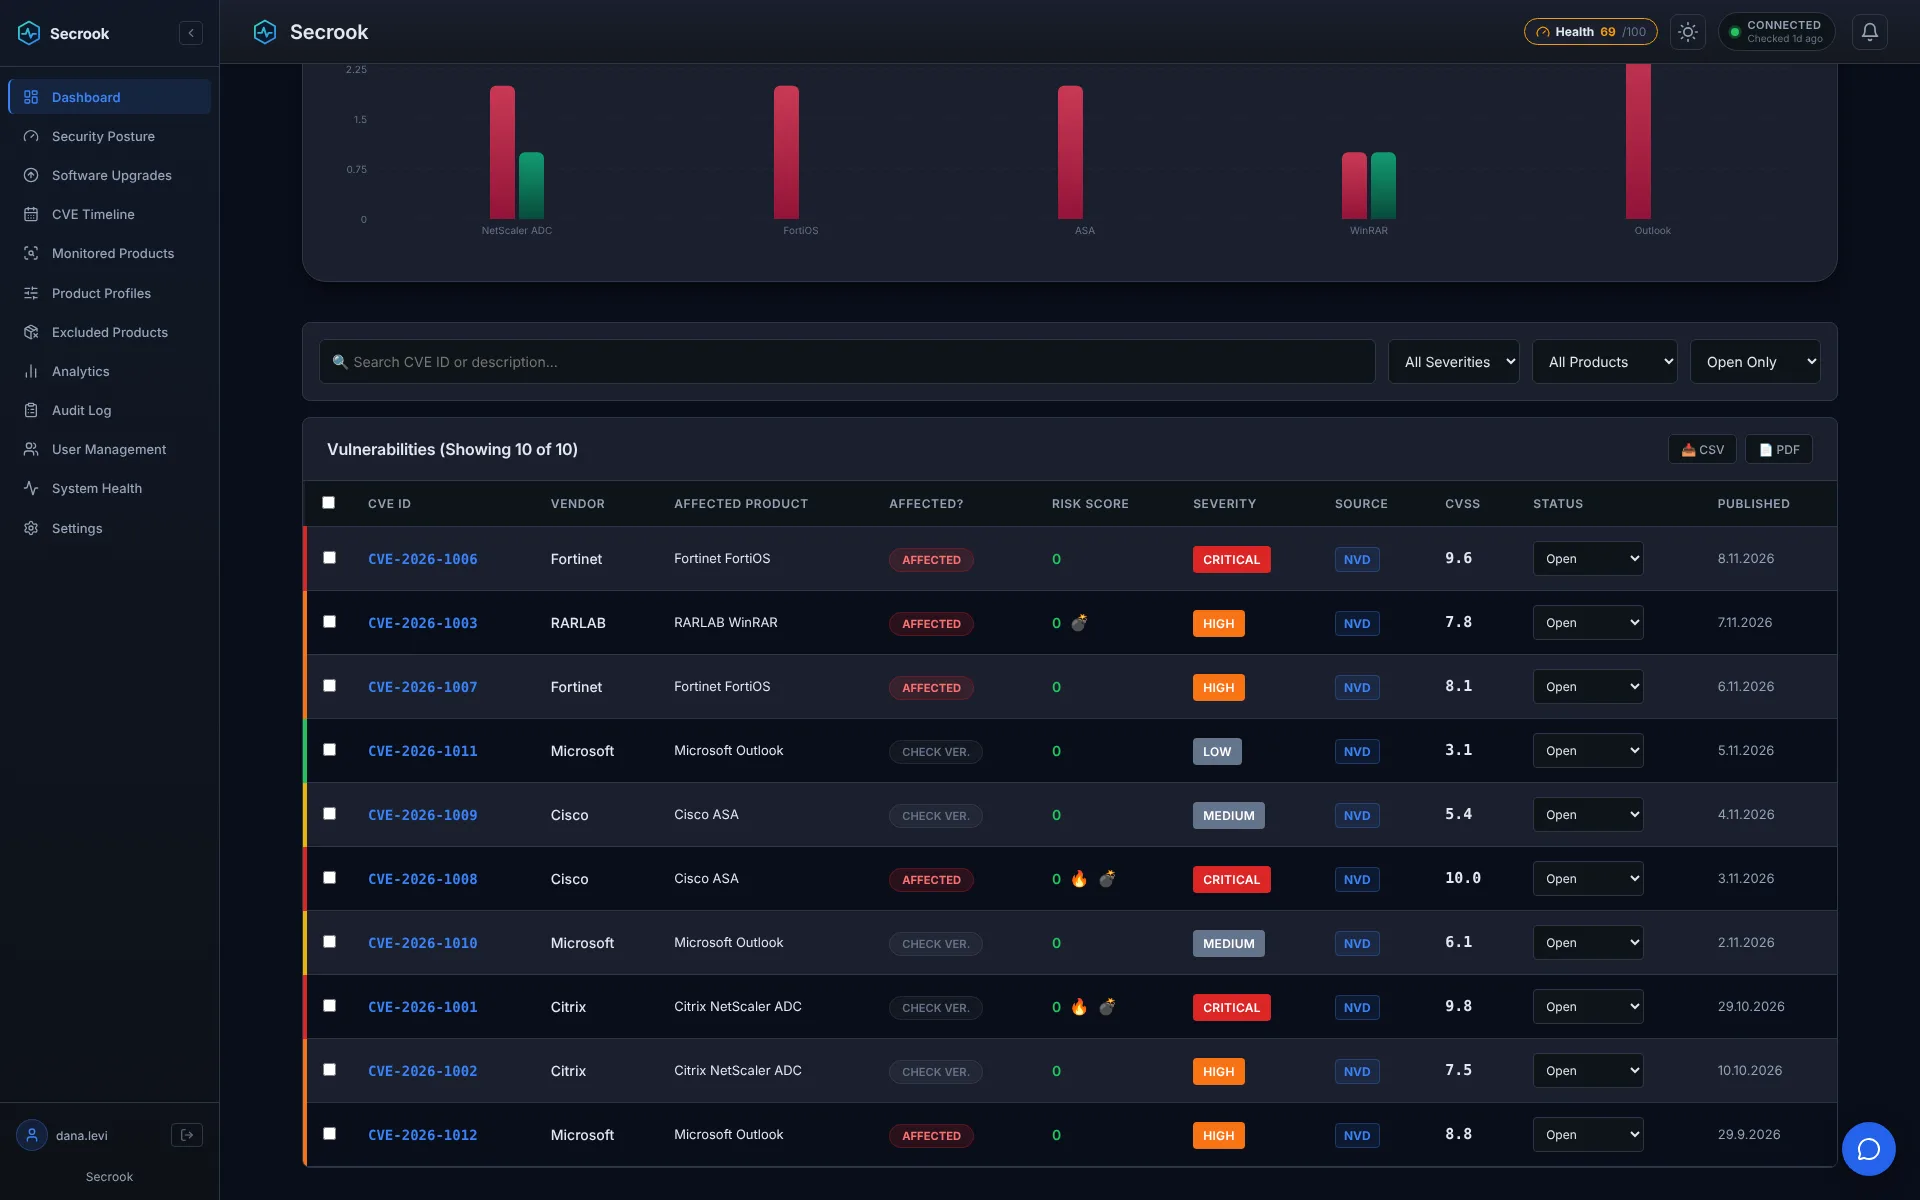
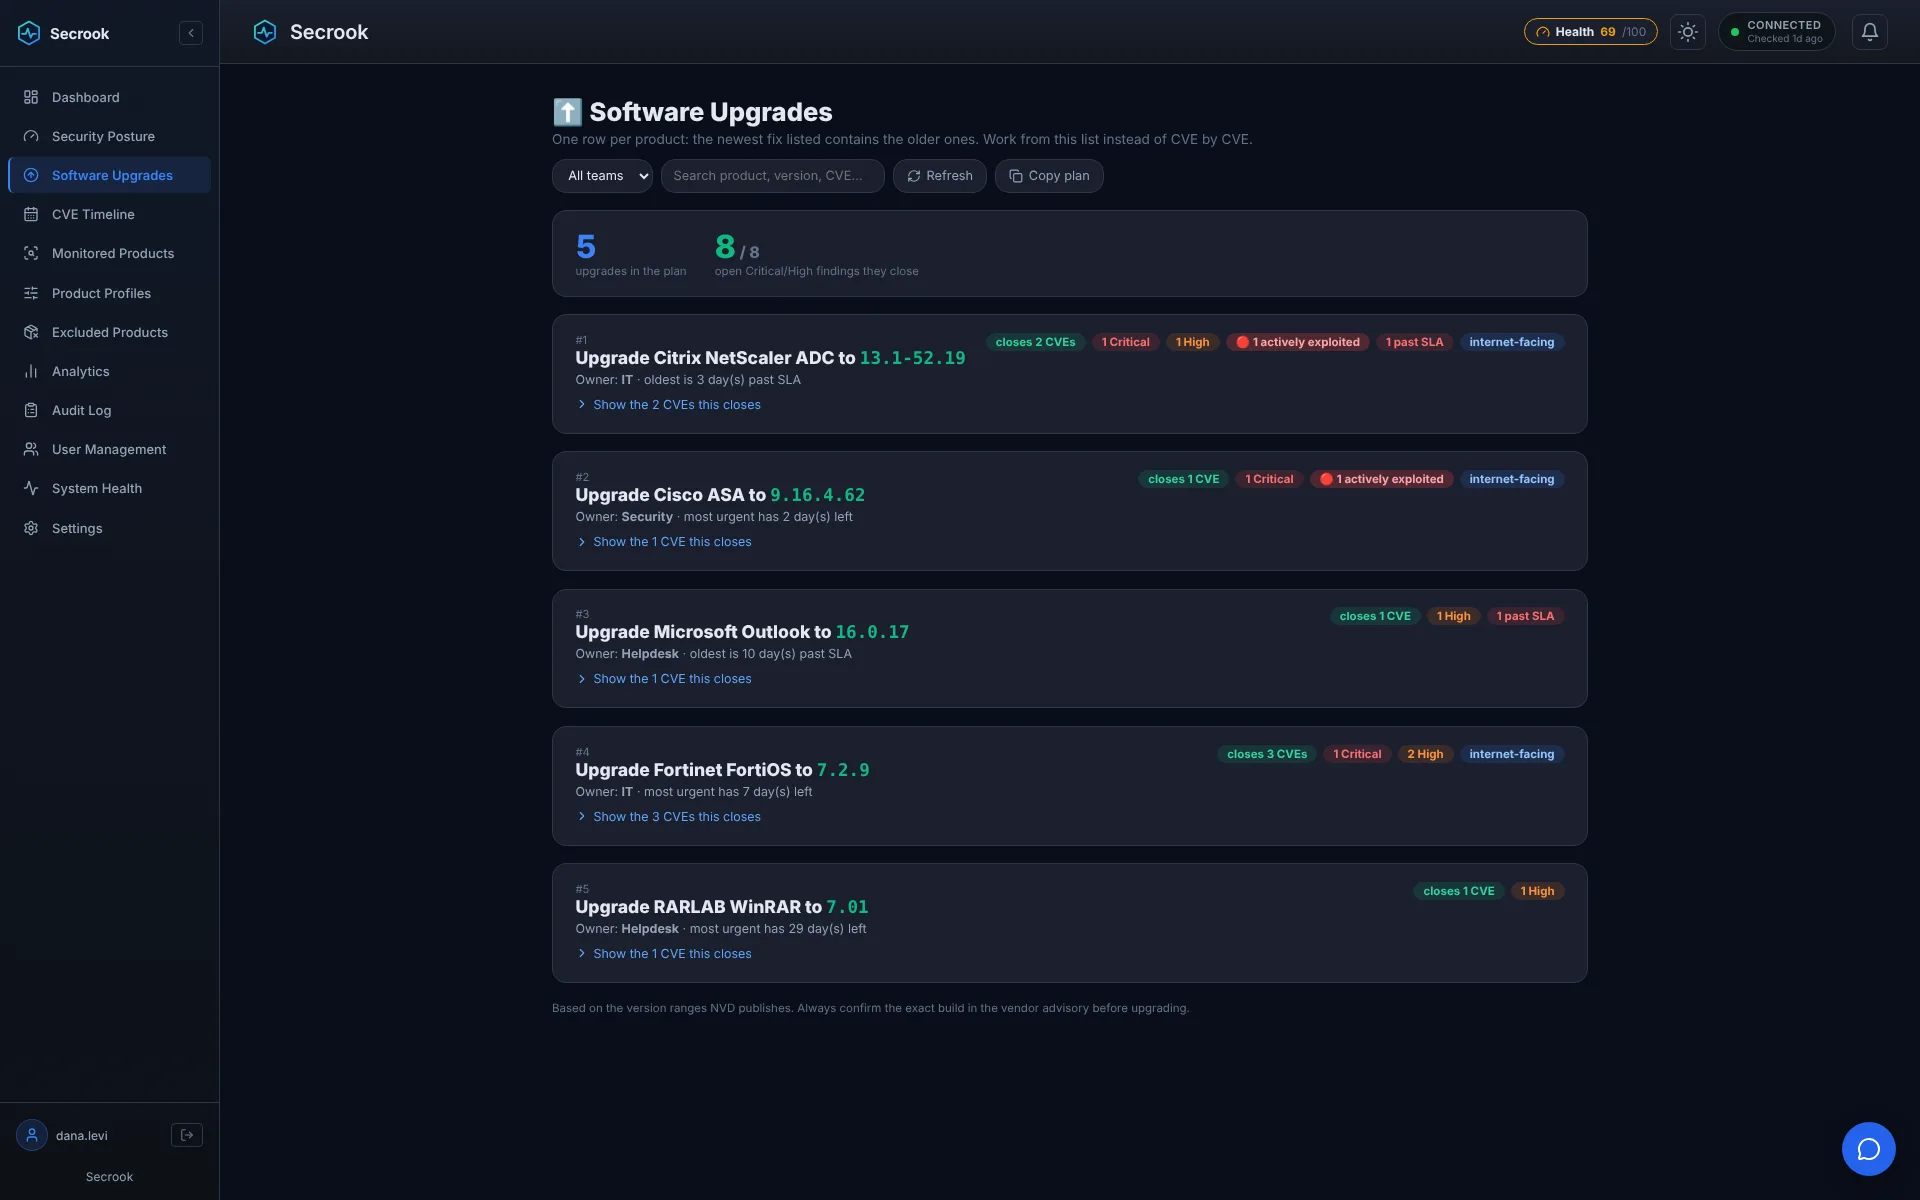
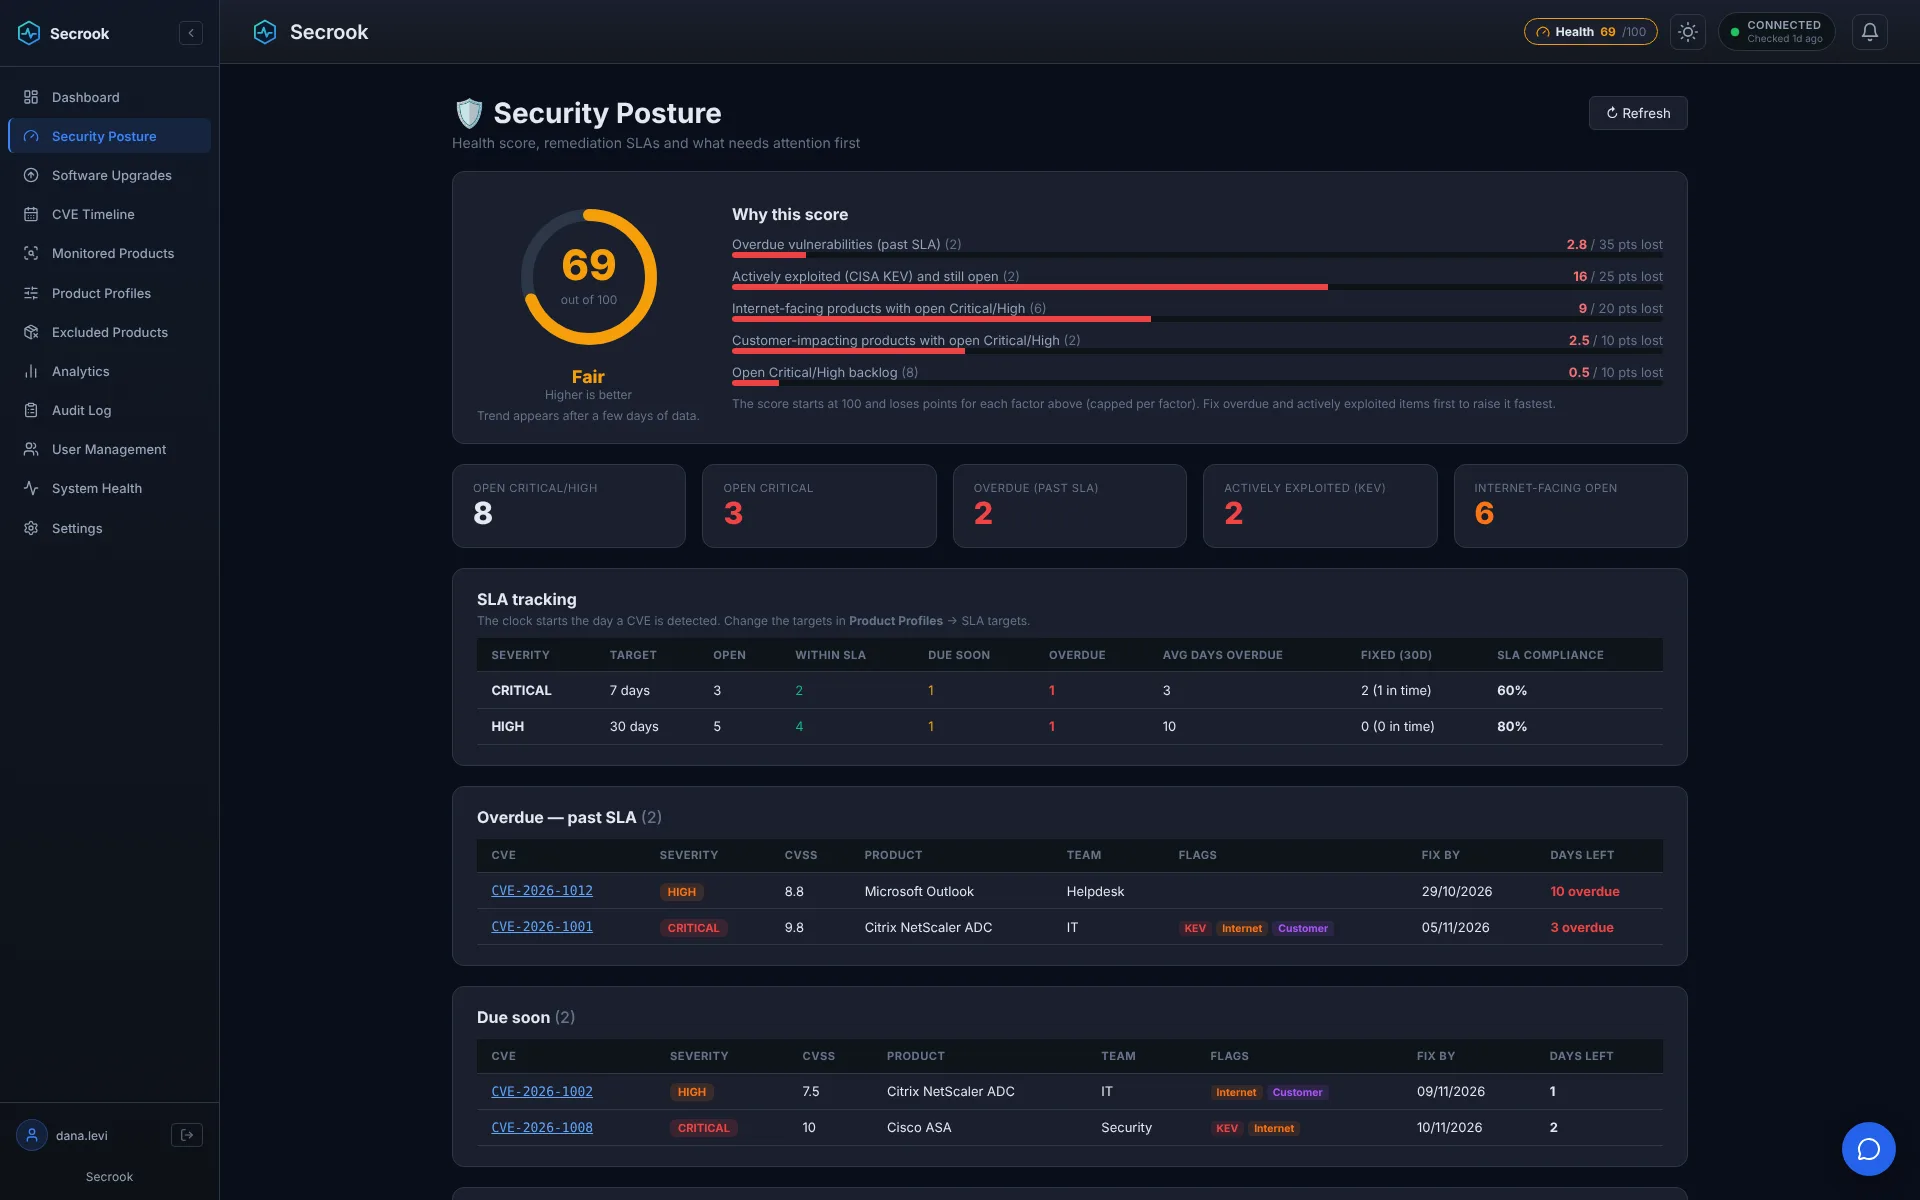
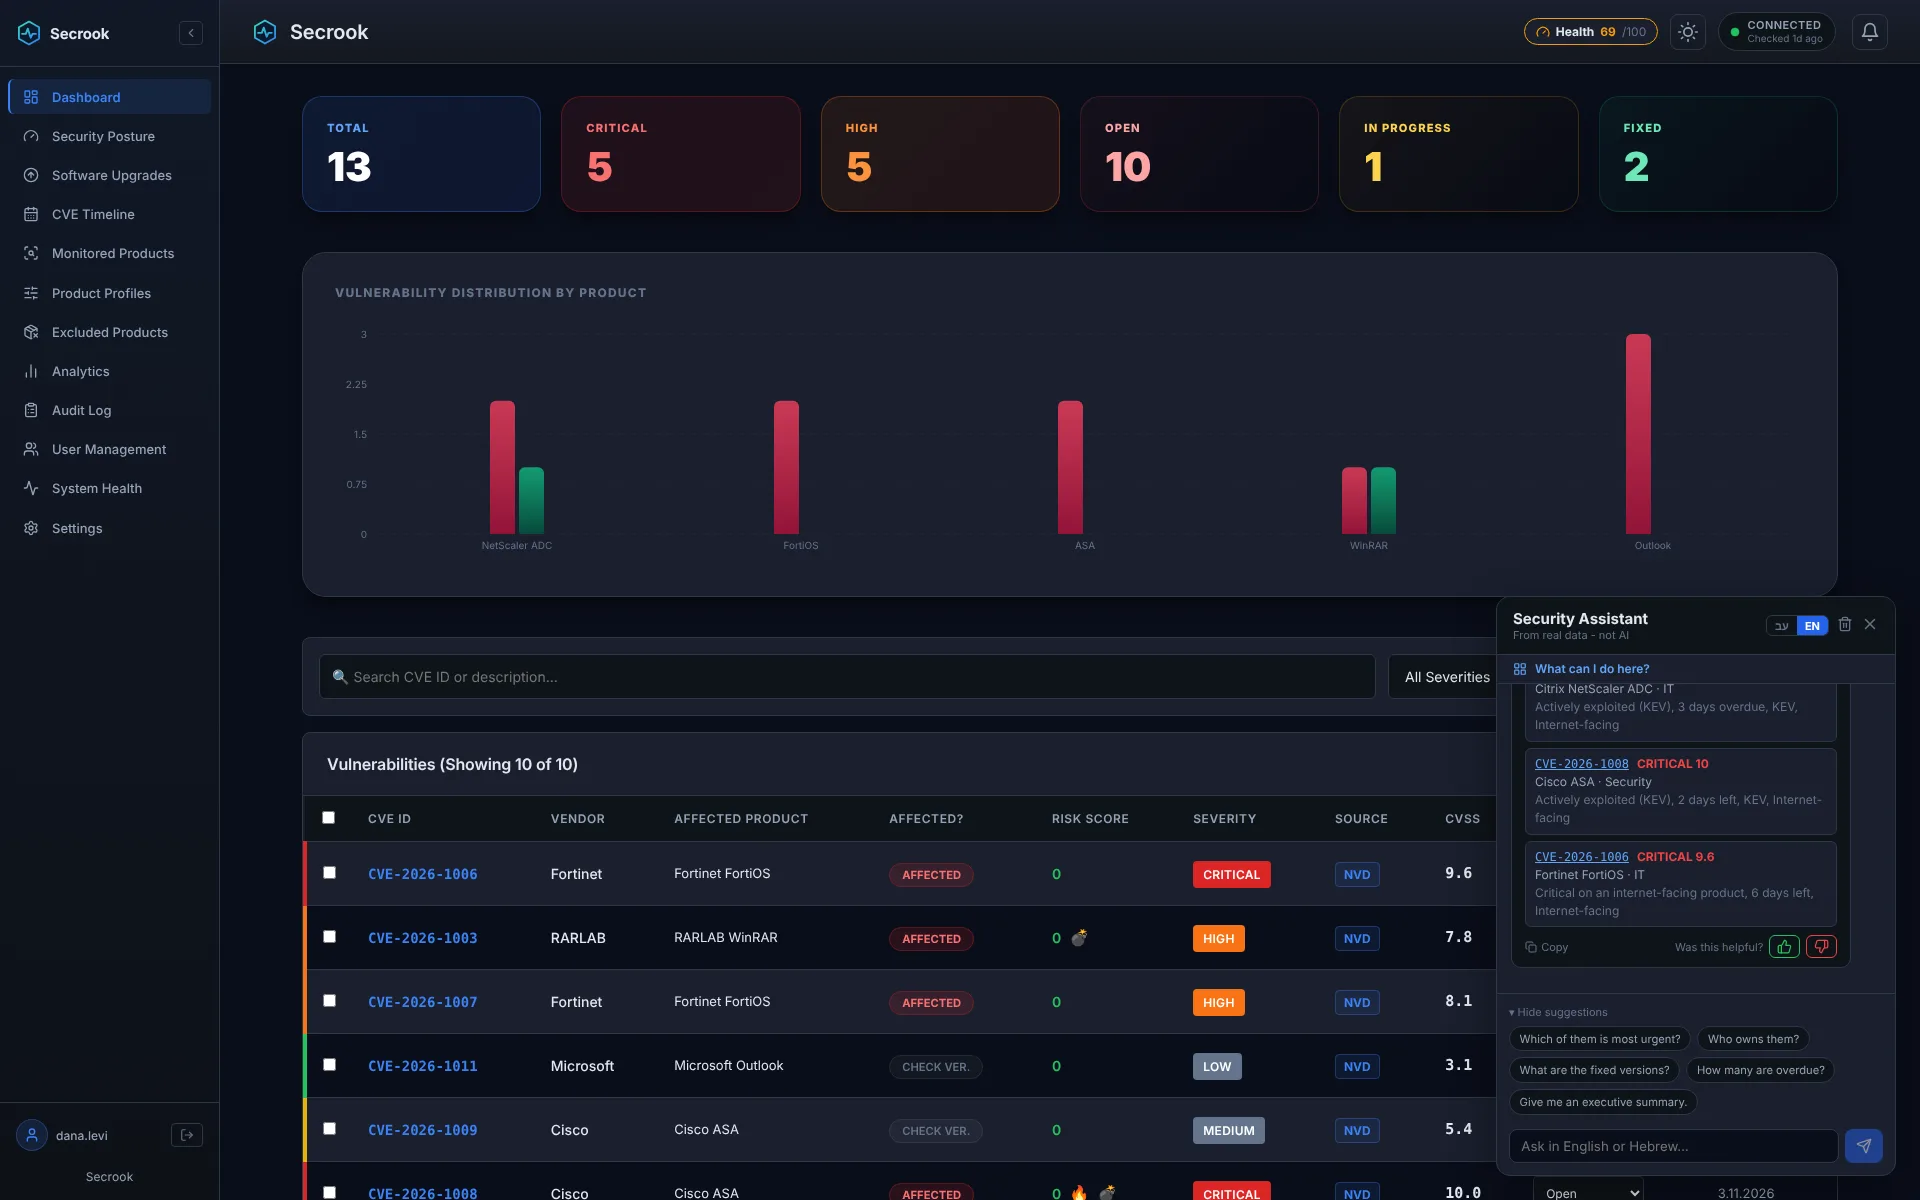
See what your team sees
Real screens from the product, with example data.
Built for teams that do not have a full-time security analyst
Plain-language explanations
Every CVE has a short "what this means for us" text, so a system owner can understand it without reading the advisory.
A clear upgrade plan
Instead of forty separate findings, see one target version per product that closes them all.
Messages ready to send
The Assistant drafts the email to the owning team, in English or Hebrew, and opens it in your mail client.
Simple plans, one price per company
No charge per asset or per application. Every plan starts with a 7-day trial.
Normal
For a small team that wants a reliable watchlist.
- Up to 15 monitored products
- 5 users, 3 teams
- Hourly alerts and email
- Keyword Assistant
Pro
For teams that need ownership, reports and an upgrade plan.
- Up to 30 monitored products
- 25 users, 15 teams
- Security Posture and Software Upgrades
- Assistant with message drafts and AI mode
Max
For enterprises with many teams and sign-in requirements.
- Unlimited products, users and teams
- Active Directory sign-in
- Audit log and API access
- Assisted install and quarterly review
Every plan starts with a 7-day trial. There is no free plan.
Find out what matters on your own products
Send us the list of products you run. We will show you the findings for the last 30 days in a short demo.